
Short answer
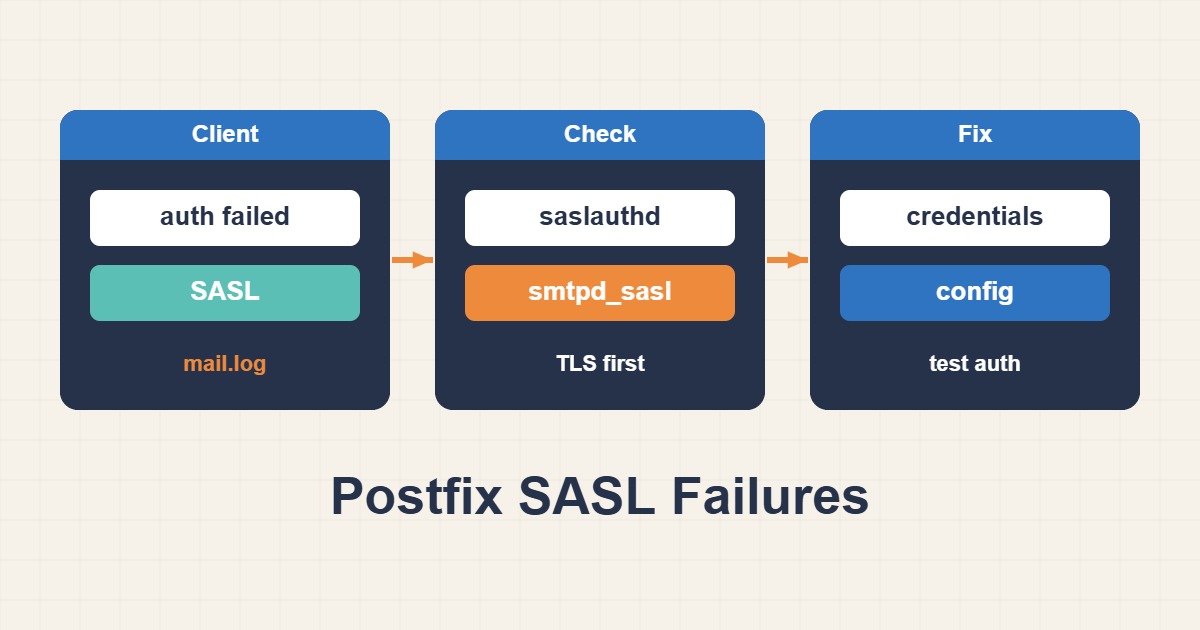
Postfix SASL authentication failures can occur on the receiving smtpd side or while the Postfix smtp client authenticates to a relay. Identify the direction, port, mechanism, and authentication backend first. Then test the socket, credential map, TLS, and permissions separately instead of changing every parameter at once.
Identify client-side versus server-side SASL
smtpd_sasl authenticates incoming users; smtp_sasl authenticates Postfix to an outbound relay. Read the process name and parameter prefix in logs.
postconf -n | grep -E "^(smtp|smtpd)_sasl|^relayhost|^smtpd_tls"
journalctl -u postfix --since "30 min ago"
Verify the authentication socket
With chrooted Postfix, the Dovecot auth socket normally lives under private/ in the queue directory and must be reachable by Postfix.
postconf queue_directory
postconf smtpd_sasl_path
ls -l /var/spool/postfix/private/auth
doveadm auth test user@example.com
Rebuild the relay credential map securely
The sasl_passwd key must exactly match relayhost, including brackets and port. Keep files mode 600 and rebuild the map after editing.
sudo postmap /etc/postfix/sasl_passwd
sudo chmod 600 /etc/postfix/sasl_passwd*
postmap -q "[smtp.example.com]:587" hash:/etc/postfix/sasl_passwd
Test TLS and the submission port
SASL is commonly offered on port 587 after STARTTLS. Inspect capabilities and the certificate chain.
openssl s_client -starttls smtp -connect smtp.example.com:587 -servername smtp.example.com
swaks --server smtp.example.com --port 587 --tls --auth
Align SASL mechanisms
No worthy mechs appears when server and client policies share no allowed mechanism. Align policy without removing transport encryption.
postconf smtp_sasl_security_options
postconf smtp_sasl_tls_security_options
Practical checklist
- Identify smtp or smtpd direction.
- Check the socket or password map.
- Test port and STARTTLS.
- Match relayhost brackets and port.
- Monitor queue and logs after reload.
Frequently asked questions
Why does a correct password still fail?
The sasl_passwd key may not match relayhost:port, or the database map was not rebuilt after editing.
Is SASL safe without TLS?
Common mechanisms do not independently protect credentials; use validated TLS for submission.
Why does an existing socket return permission denied?
The Postfix chroot or service user may lack access to a parent directory or the socket itself.
How to verify the fix
A swaks or real-client test should authenticate, permit relay for the authorized user, and log status=sent for a test message. An invalid login must still fail, and open relay must remain impossible.
Risks and rollback
Back up main.cf, master.cf, and sasl_passwd. Never expose credentials in public logs. Roll back by restoring files, rebuilding the map, running postfix check, and reloading.
Anonymized field scenario
After a relay change, valid credentials still returned 535. The map key omitted the submission port. Matching [host]:587 and rebuilding the map made both the TLS test and real delivery succeed.
Related guides
Official documentation
{L[8]}: {DATE}
Conclusion
Confirm the cause from logs and metrics, change one variable, and measure again under representative load.