
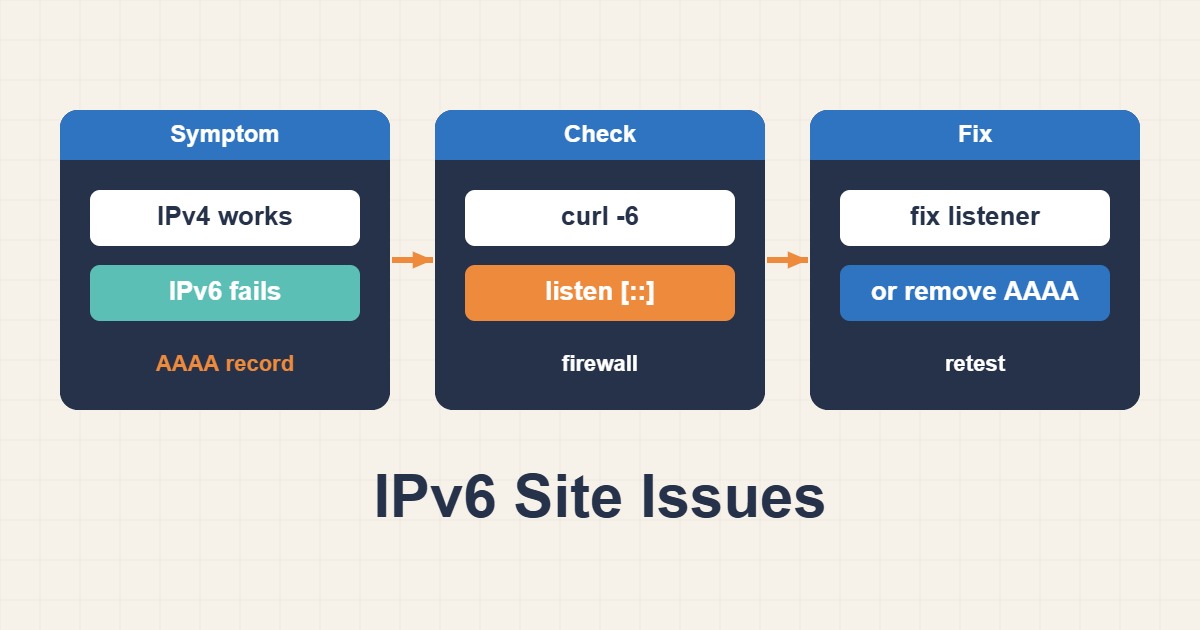
Missing routing, listeners or IPv6 firewall rules can cause timeouts for part of the audience. Test each address family independently from DNS through TLS so browser fallback does not hide a broken deployment.
Scope and prerequisites
The test client needs genuine IPv6 connectivity; curl -6 failure on a client without a route does not prove a site fault. Record A/AAAA records and CDN mode. Addresses in 2001:db8::/32 are documentation-only and not internet-routable; substitute an actually assigned address when testing an origin.
1. Collect evidence
Compare DNS resolution, TCP and TLS using curl -4 and -6 against the same hostname. On the origin, inspect global addresses, default routing and listening sockets. A CDN may provide IPv6 at the edge while using IPv4 to the origin; public and origin paths are not necessarily identical.
dig +short A example.com
dig +short AAAA example.com
curl -4 -I --connect-timeout 5 https://example.com/
curl -6 -I --connect-timeout 5 https://example.com/
ip -6 addr show
ip -6 route show
sudo ss -lntp
2. Make a controlled change
Add the IPv6 listener to the existing valid server block while retaining certificates and server_name. Host firewall, security groups and provider routing all need IPv6 coverage. Do not blindly block essential ICMPv6 used by network operation and path-MTU discovery. Advertise DNS only after the path is working.
# Add within the EXISTING HTTPS server block; preserve TLS settings.
listen 443 ssl;
listen [::]:443 ssl;
3. Verify the outcome
Validate and reload, then test IPv6 HTTPS from two independent networks. Certificates, redirects and response bodies should match IPv4 behavior. curl --resolve targets a specific address while preserving hostname and SNI. A bare-IP request without SNI can hit the wrong virtual host and mislead diagnosis.
sudo nginx -t && sudo systemctl reload nginx
# Replace documentation IP with your assigned origin IPv6 address.
curl -6 --resolve "example.com:443:[2001:db8::10]" -I https://example.com/
Rollback and prevention
If IPv6 is not ready, temporarily withdrawing AAAA with awareness of TTL and CDN policy can mitigate impact, but does not repair routing. Do not disable IPv6 host-wide. Restore the record after repair and monitor IPv6 separately; an IPv4-only healthcheck cannot prove availability for every user.
Technical references
For related checks in this workflow, see Split-Horizon DNS with BIND: Internal and Public Answers and Diagnose Linux Packet Loss and Path MTU Problems.